
Who is it for
Security leadershipDesigning or maturing ISMS programs.
Executive reportingOrganizations needing governance and reporting that is leadership-ready.
Enterprise alignmentAligning security, compliance, and incident response.
Design, mature, or modernize your security program with governance that stays audit-ready and aligned to day-to-day operations.

A voiced, cinematic walkthrough of 3HUE's managed programs — led by Ava, your guide. Choose your path, ask questions along the way, and leave with a summary in your inbox.
Security leadershipDesigning or maturing ISMS programs.
Executive reportingOrganizations needing governance and reporting that is leadership-ready.
Enterprise alignmentAligning security, compliance, and incident response.
Weekly working sessions and monthly governance reviews.
vCISO leadership, GRC analysts, incident response specialists.

Summaries of each managed program component and leadership option.
Builds a formal security program aligned to frameworks like SCF, NIST, or ISO for consistent controls and audit readiness.
Establishes risk management to identify, prioritize, and mitigate security risk with a risk-informed culture and tracking.
Manages third-party risk by aligning vendor practices to risk tolerance, contractual controls, and regulatory expectations.
Delivers response planning and incident command services with clear roles, escalation paths, and coordinated recovery.
Executive security leadership integrated with your team to shape strategy, guide decisions, and oversee compliance.
Flexible senior CISO support as staff augmentation for organizations that do not need a full-time executive.
Core security governance capabilities mapped to common regulatory and assurance frameworks.
| Standards alignment focus | ISO 27001 | SOC 2 | FedRAMP | CMMC | HITRUST | HIPAA |
|---|---|---|---|---|---|---|
| Security governance and defined program scope | ||||||
| Security policies, standards, and procedures approved and maintained | ||||||
| Asset inventory and data classification maintained | ||||||
| Risk assessment performed and tracked on a defined cadence | ||||||
| Change management and secure configuration baselines |
Design, mature, or modernize your information security and GRC program with proven frameworks and continuous operational alignment.
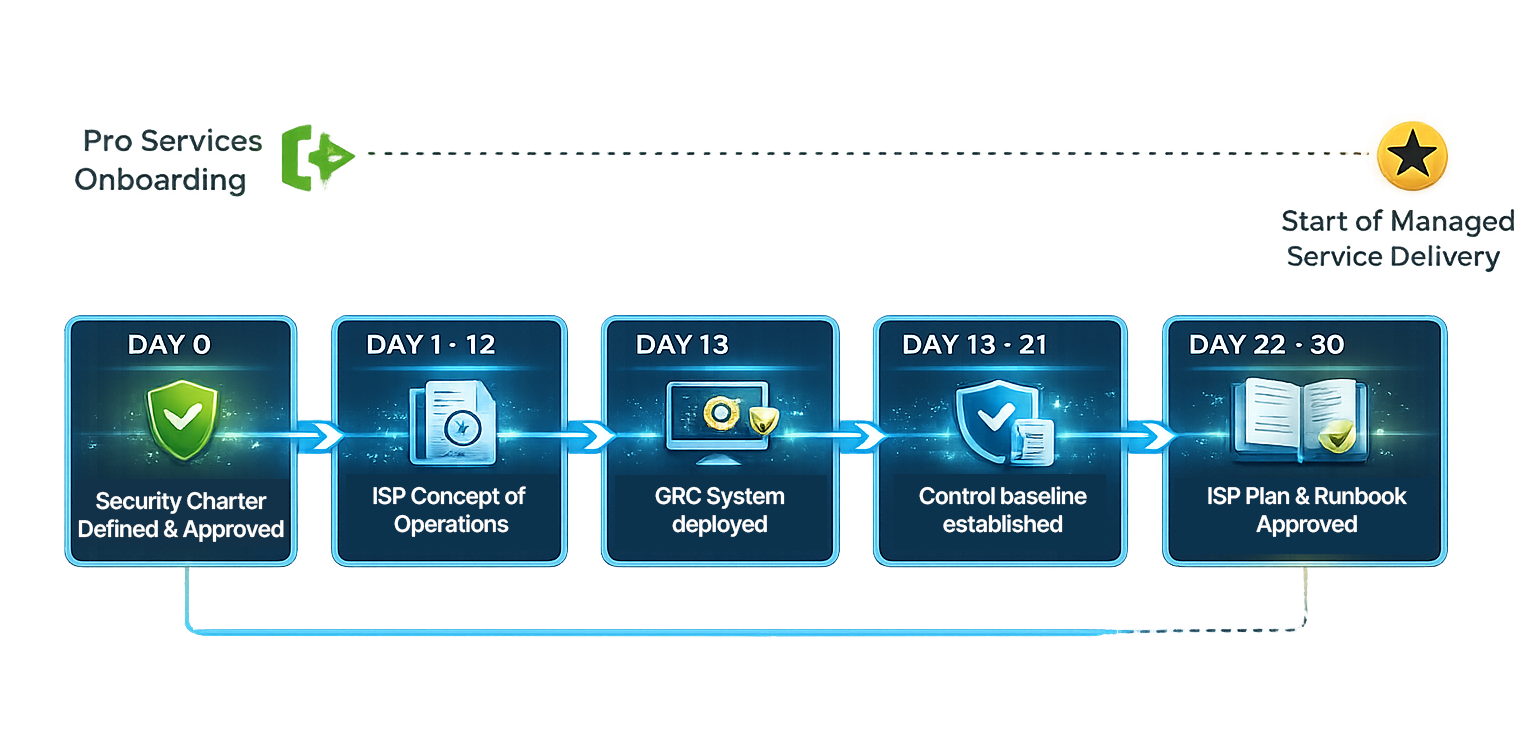
All ISG managed programs — ISP, RMP, CIRP, VCP, and vCISO — can now be delivered on the AiVRIC CloudSignals+ RiskOps platform. This is our recommended delivery path for 2026 and beyond: agentic AI doing the heavy lifting, every action gated by a senior 3HUE practitioner.
The result is governed acceleration — AI velocity under an expert gate. Your program runs continuously rather than periodically, evidence is automated and timestamped, and the audit trail is built in by design. Faster, deeper, and just as defensible as the traditional path.
Audit readiness means your security program, policies and evidence are already in place and working before the auditor arrives, so the audit confirms what you do instead of uncovering gaps.
ISO 27001, SOC 2, CMMC, HIPAA and FedRAMP. We build one program and map it to the frameworks you need.
It depends on your starting point and the framework. We baseline your current state first, then set a timeline for closing the gaps.
Request a consult or download the program overview.